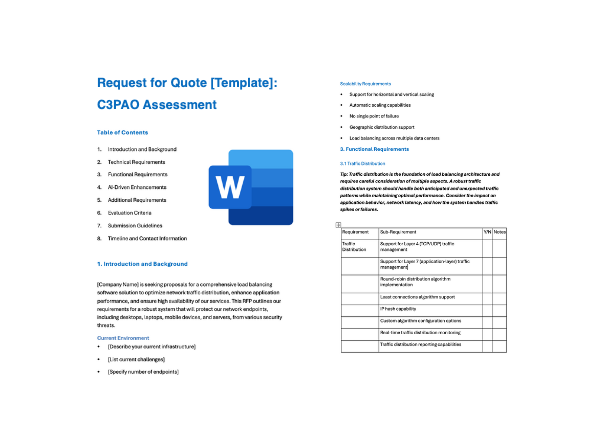
How to run a C3PAO RFQ
A C3PAO assessment covers one defined scope, so this template is a request for quote (RFQ) rather than a full RFP: you describe that scope once, send the same RFQ to several C3PAOs, and compare what each would do, who would do it, when, and at what price. Check the DoD CIO's CMMC page before you start, since the program's status affects whether you want an assessment now. The timeline table in the Word document has a row for each milestone, ready for your own dates.
- Write down why you want an assessment, and what's in scope. List what's driving the decision, such as a request from a customer or prime contractor, or a decision to get an independent view of your Level 2 implementation. Then record your CMMC Assessment Scope, the state of your system security plan, any Level 2 self-assessment and affirmation you have entered in SPRS, your locations, and the outside providers whose services are in scope. C3PAOs will quote against this, so put it in the background section of the RFQ.
- Assemble the buying team. Include the executive who owns the decision, the IT or security lead who owns the system security plan, whoever manages your DoD contracts, and finance. Add legal for the confidentiality agreement and the contract terms. Keep any consultant that helped you prepare, and the outside providers in your scope, informed and available, but keep the choice of C3PAO with your own team.
- Decide what you're buying, and whether you need an RFI. Decide whether you want a readiness review, a certification assessment, or both, and whether you are open to buying them from different firms. Before you decide, ask each C3PAO how it applies the Accreditation Body's conflict-of-interest policy to readiness work and assessments for the same organization. If the choice is still open, or you want to narrow a long list, send a short RFI asking each C3PAO for its authorization, how it is handling assessments while Phase II is suspended, its availability, and any past work for you.
- Build a shortlist from the CMMC Marketplace. RFPhub doesn't list C3PAOs. Find them on the Cyber AB's CMMC Marketplace, and note each one's name exactly as listed so you can confirm its authorization again before award. Sign a confidentiality agreement with each shortlisted C3PAO before you share details of your scope or your system security plan.
- Tailor and issue the RFQ. Delete requirements that don't apply, adjust the priorities, and describe the same scope to every C3PAO so the quotes can be compared. Ask for separate prices for the readiness review, the assessment and any POA&M close-out review. Set a response deadline with a written question-and-answer window, and share every answer with all the C3PAOs you invited.
- Score the quotes and talk to the lead assessors. Have each evaluator score independently against the rubric before comparing notes, and set aside any quote that misses a Must-have. Hold a call with each shortlisted C3PAO's proposed lead assessor, give each the same scenario, such as a system found outside your scope partway through the assessment, and compare the answers.
- Confirm authorization and award. Check the CMMC Marketplace again for the C3PAO you choose before you sign. Write the assessment team, the schedule, the evidence handling rules, the disclosures of past work for you, the fees and the rescheduling terms into the contract or statement of work.
C3PAO RFQ requirements
Each line is written to paste straight into your RFQ. Must-have means a provider that cannot meet it is out; Nice-to-have earns extra points. Change the priorities to fit your situation, and delete what doesn't apply.
Scope of services
| ID |
Requirement |
Priority |
| S1 |
A CMMC Level 2 certification assessment of our organization as an Organization Seeking Certification (OSC), covering the CMMC Assessment Scope set out in our system security plan and summarized in the background section of this RFQ. |
Must-have |
| S2 |
A review of our CMMC Assessment Scope and system security plan before the assessment is scheduled, with any questions or concerns about the scope raised in writing before assessment work begins. |
Must-have |
| S3 |
An optional pre-assessment readiness review, priced separately, that identifies requirements where our implementation, documentation or evidence may not be ready. State who would deliver it (your organization, an affiliate or another firm) and whether buying it would affect your ability to conduct our certification assessment. |
Nice-to-have |
| S4 |
A plan for the parts of our CMMC Assessment Scope that outside providers, such as our MSP or cloud provider, operate for us [if applicable]: the evidence you would need from each provider, and how you would arrange access to their people and documents. |
Must-have |
| S5 |
A closing briefing for our team at the end of the assessment, and the assessment results in writing, listing each requirement found not met and the reason. |
Must-have |
| S6 |
Submission of the assessment results and any Certificate of CMMC Status into the CMMC instantiation of eMASS, as 32 CFR 170.9(b)(8) requires, so the results reach SPRS. |
Must-have |
| S7 |
A statement of how you handle requirements found not met, including whether you would conduct a POA&M close-out review, what it would cover, and how you would schedule it. |
Must-have |
| S8 |
If we have more than one CMMC Assessment Scope [if applicable], a statement of whether you would assess them together or separately, with a price for each. |
Nice-to-have |
Named lead and team
| ID |
Requirement |
Priority |
| L1 |
The name of the lead assessor for our assessment and of each other team member, with each person's role, qualifications and experience assessing organizations like ours. |
Must-have |
| L2 |
Confirmation that every person taking part in our Level 2 certification assessment has completed a Tier 3 background investigation or, where not eligible, meets DoD's equivalent, as 32 CFR 170.9(b)(3) requires. |
Must-have |
| L3 |
A statement of which team members are employees of the C3PAO and which are subcontractors, and of any part of the work that another organization would do. |
Must-have |
| L4 |
Written notice before any change to the named lead assessor or team, with the replacement's qualifications and confirmation of their background investigation, and time for us to raise concerns before the change takes effect. |
Must-have |
| L5 |
Experience assessing organizations similar to ours in size, industry and type of environment (for example cloud-hosted, on-premises, hybrid or an enclave), supported by references where clients agree to be contacted. |
Must-have |
| L6 |
A single named contact for scheduling, logistics and document requests, from the start of planning until the results are submitted into eMASS. |
Must-have |
| L7 |
A call with the proposed lead assessor before we award the work, so we can discuss our scope and how the assessment would run. |
Nice-to-have |
Deliverables and reporting
| ID |
Requirement |
Priority |
| D1 |
An assessment plan agreed before work begins, setting out the scope to be assessed, the people you need to interview, the documents and system access you need, the schedule, and which work happens on site and which remotely. |
Must-have |
| D2 |
If we buy a readiness review: a written report listing each requirement where you see a gap in our implementation, documentation or evidence, written for our IT and compliance staff. |
Must-have |
| D3 |
Regular status updates during the assessment on progress, and on any evidence or interviews still needed. |
Must-have |
| D4 |
A copy of any Certificate of CMMC Status you issue, and a written statement of the resulting status (Conditional or Final Level 2 (C3PAO)) and the assessment scope it applies to. |
Must-have |
| D5 |
Written confirmation, with the date, when you have submitted our results and any certificate into eMASS. |
Must-have |
| D6 |
If a POA&M close-out review takes place: the written result of that review. |
Nice-to-have |
Security, confidentiality and independence
| ID |
Requirement |
Priority |
| N1 |
Current authorization or accreditation by The Cyber AB to conduct Level 2 certification assessments. Give your organization's name exactly as it appears on the Cyber AB's CMMC Marketplace; we will confirm your listing there before awarding work. |
Must-have |
| N2 |
Disclosure of any consulting, readiness, implementation, managed or other services that the C3PAO or any affiliate has provided to us, is providing to us, or has proposed to us, with the dates and a description of each. |
Must-have |
| N3 |
Compliance with the Accreditation Body's conflict-of-interest, professional conduct and ethics policies, as 32 CFR 170.9(b)(2) requires, and prompt written notice to us of any conflict of interest that arises during the engagement. |
Must-have |
| N4 |
A statement of the C3PAO's status against ISO/IEC 17020:2012, which 32 CFR 170.9(b)(2) requires C3PAOs to achieve within a set period after authorization and then maintain, and notice to us if that status changes before our assessment is complete. |
Must-have |
| N5 |
Fees that do not depend on the result of the assessment. |
Must-have |
| N6 |
Evidence handling rules agreed before the assessment: what your team will copy and what it will only view in our environment, where copies are stored, who can access them, how they are protected in transit and at rest, and how they are returned or destroyed, apart from records you must keep. |
Must-have |
| N7 |
A statement of the assessment records you will keep about us, including those that 32 CFR 170.9(b)(9) requires you to keep for six years, and how you protect them. |
Must-have |
| N8 |
Confidentiality terms covering everything your team learns about our systems, security, contracts and people, signed before we share our system security plan or other details of our scope. |
Must-have |
| N9 |
Access to our systems only through accounts we issue to named team members, with multifactor authentication, the least privilege needed and read-only access where possible, all removed when the assessment ends. |
Must-have |
| N10 |
A description of how the C3PAO protects client data on its own systems and staff devices, a commitment to notify us of any security incident affecting our data within a defined time (state the time), and professional liability and cyber liability insurance with the coverage limits stated. |
Must-have |
Engagement and transition
| ID |
Requirement |
Priority |
| E1 |
A written statement of how you are handling Level 2 certification assessments while Phase II is suspended, including any terms, dates or prices in your quote that would change if the program's requirements change. |
Must-have |
| E2 |
A proposed schedule for each stage (the readiness review if we buy one, assessment planning, on-site and remote assessment work, the closing briefing and results entry into eMASS), with the earliest start date you can offer. |
Must-have |
| E3 |
A statement of which locations need on-site work [list locations], what can be done remotely, and what you need from us for remote sessions, such as video calls, screen sharing and document access. |
Must-have |
| E4 |
A list of what you need from us before and during the assessment: documents, the people to interview and when, system access, workspace on site, and a single point of contact on our side. |
Must-have |
| E5 |
Rescheduling and cancellation terms for both sides, including what happens to the schedule and the fees if we are not ready on the agreed date or the assessment has to pause. |
Must-have |
| E6 |
Your process for handling a disagreement with a finding, during and after the assessment, and who in your organization makes the decision. |
Must-have |
| E7 |
A statement of whether you would assess a later change to our CMMC Assessment Scope, such as a new location or system, and how you would scope and price that work. |
Nice-to-have |
| E8 |
Termination by either side with written notice, with fees limited to work done up to that point. |
Must-have |
Commercial and pricing
| ID |
Requirement |
Priority |
| C1 |
A fixed fee for the Level 2 certification assessment of the scope described in this RFQ, stating what is included and what would change the fee. |
Must-have |
| C2 |
A separate fixed fee for the optional pre-assessment readiness review, so we can buy the assessment without it. |
Must-have |
| C3 |
A separate price for any POA&M close-out review, stating what it covers and whether it is a fixed fee or charged by time. |
Must-have |
| C4 |
Daily rates for each role for extra work caused by a scope change we approve, with no extra time billed unless we approve it in writing first. |
Must-have |
| C5 |
A travel and expenses policy for on-site work, with an estimate for each visit agreed with us before travel is booked. |
Must-have |
| C6 |
A payment schedule tied to milestones, such as the agreed assessment plan, the closing briefing and results entry into eMASS. |
Must-have |
Questions to ask C3PAO providers
These questions are designed to separate providers, not to collect brochure answers. Ask for evidence: a sample deliverable, an interview with the named lead or a reference.
- Give your organization's name exactly as it appears on the Cyber AB's CMMC Marketplace, and confirm that you are currently authorized or accredited to conduct Level 2 certification assessments. We will check the Marketplace before awarding work.
- How are you handling Level 2 certification assessments while Phase II is suspended? Tell us what, if anything, has changed in your scheduling, terms or pricing, and how you would handle a change to the program's requirements during our engagement.
- How do you apply the Accreditation Body's conflict-of-interest policy to an engagement like ours? List any consulting or other services you or an affiliate have provided to us, and tell us whether a readiness review by you would affect your ability to conduct our certification assessment.
- Review the summary of our CMMC Assessment Scope and system security plan in the background section. What questions or concerns would you raise before scheduling the assessment, and what more would you need from us?
- Walk us through our assessment from kickoff to results entry in eMASS: each stage, who from your team is involved, what you need from us, and which work happens on site and which remotely.
- Partway through the assessment, your team finds that a system we left out of our CMMC Assessment Scope handles information that should be in it. What would you do, and how would it affect the schedule, the result and the price?
- Evidence for several requirements is held by our MSP and our cloud provider. How would you assess those requirements, what would you need from each provider, and who arranges it?
- If your team finds requirements not met, what happens next? Explain what would lead to a Conditional rather than a Final Level 2 (C3PAO) status, how a POA&M close-out review would work with you, and how you would price it.
- Describe how your team handles our evidence: what you copy, what you only view in our environment, where copies are stored, who can access them, and which records you keep about us afterward.
- Confirm that each person on the proposed team has completed a Tier 3 background investigation or meets DoD's equivalent. Who is an employee and who is a subcontractor, and what happens if the lead assessor becomes unavailable shortly before our assessment?
- If we disagree with a finding, what is your process during the assessment and after it, and who in your organization makes the decision?
- Send a redacted sample or a blank template of the assessment plan, status update and readiness review report you would deliver to us.
- What is the earliest date you could start our assessment, and what on our side or yours could move it?
- Provide a reference from an organization of similar size and environment that you have assessed and that has agreed to be contacted.
Scoring rubric
Score each criterion from 1 to 5, multiply by its weight, and add the results. The weights below are a starting point; agree on your own before any quotes arrive so the scoring can't be bent around a favorite.
| Criterion |
Weight |
What a strong response shows |
| Assessment team qualifications and fit |
20% |
A named lead assessor and team with relevant qualifications and experience with organizations of your size and environment, confirmed Tier 3 background investigations or DoD's equivalent, and a clear split of employees and subcontractors. |
| Assessment plan and approach to your scope |
20% |
A specific plan for your CMMC Assessment Scope and outside providers, useful questions about your system security plan, a clear list of what's needed from your team, and sensible answers to the scope and evidence scenarios. |
| Independence and conflict-of-interest handling |
15% |
Full written disclosure of any past work for you by the C3PAO or an affiliate, a clear explanation of how it applies the Accreditation Body's conflict-of-interest policy, and fees that do not depend on the result. |
| Evidence handling and confidentiality |
10% |
Clear rules for what is copied and what stays in your environment, protected storage and access, a stated approach to record retention, and access to your systems only through named accounts. |
| Schedule, logistics and program status |
10% |
A workable schedule with an earliest start date, a clear split of on-site and remote work, rescheduling terms that are fair to both sides, and a direct answer on how assessments are handled while Phase II is suspended. |
| Findings, POA&M and results handling |
10% |
A clear explanation of how findings are recorded and briefed, what would lead to a Conditional or a Final status, how any POA&M close-out review works, how disagreements are handled, and confirmation of results entry into eMASS. |
| Commercials and value |
15% |
Separate fixed fees for the readiness review, the assessment and any POA&M close-out review, a stated expenses policy, fair rates for approved extra work, and milestone payments. |
| Total |
100% |
|
Scoring scale
- 5 Exceeds: meets every Must-have and most Nice-to-haves, shown through an interview with the named lead, sample deliverables and a matching reference client.
- 4 Strong: meets every Must-have and some Nice-to-haves, with clear evidence.
- 3 Adequate: meets most Must-haves; gaps have a credible plan.
- 2 Weak: misses one or more Must-haves, or the answer is vague.
- 1 Poor: does not meet the requirement, or no answer.
Frequently asked questions
What is a C3PAO?
A C3PAO (CMMC Third-Party Assessment Organization) is an organization authorized or accredited by the Accreditation Body, The Cyber AB, to conduct CMMC Level 2 certification assessments (32 CFR 170.4). C3PAOs conduct those assessments, issue Certificates of CMMC Status to Organizations Seeking Certification, and submit results and certificates into the CMMC instantiation of eMASS, which passes the results to SPRS (32 CFR 170.9 and 170.17). A Level 2 certification assessment can result in a Conditional or a Final Level 2 (C3PAO) status, and Level 2 (C3PAO) status also satisfies Level 1 (Self) and Level 2 (Self) for the same assessment scope (32 CFR 170.17). RFPhub doesn't list C3PAOs: the official list is the Cyber AB's CMMC Marketplace, so use it to find C3PAOs and confirm each one's authorization before you award work.
Is CMMC Phase II suspended?
As of November 2026, the DoD CIO's CMMC page (dodcio.defense.gov/CMMC/About/) says Phase 1 implementation began on November 10, 2025, and that on July 13, 2026 the DoD suspended Phase II, which had been scheduled for November 10, 2026, and set up a CMMC reform task force. The program is paused in Phase 1: Level 1 and Level 2 self-assessments, with annual affirmations in SPRS, and the requirement to protect information under DFARS clause 252.204-7012 still applies. Check that page and your contracts for what applies to you. Some organizations may still choose a C3PAO assessment or readiness work; if you do, ask each C3PAO how it is handling assessments while Phase II is suspended.
What should a C3PAO RFQ include?
Your background and CMMC Assessment Scope; the services you want quoted, such as a readiness review, the Level 2 certification assessment and any POA&M close-out review; requirements for the assessment team, deliverables, confidentiality and independence, scheduling and pricing, each marked Must-have or Nice-to-have; questions that show how each C3PAO works; and the rubric you'll score with. This template includes all of them. RFPhub's free CMMC Compliance Checklist can help you track your own readiness before you ask for quotes.
Can a C3PAO help us prepare and then assess us?
Ask each C3PAO directly, and get the answer in writing. The CMMC rule requires C3PAOs to comply with the Accreditation Body's conflict-of-interest, professional conduct and ethics policies, and to keep assessment records, including records of organizations they provided consulting services to (32 CFR 170.9(b)(2) and (b)(9)). This template doesn't summarize those policies; it asks each C3PAO to disclose any consulting it or an affiliate has done for you, and to explain how it applies the conflict-of-interest policy to your engagement.
How much does a C3PAO assessment cost?
Price depends on scope, so the useful comparison is between quotes for the same scope. The main cost drivers are the size and complexity of your CMMC Assessment Scope, the number of locations that need on-site work, how many outside providers' services are in scope, how ready your system security plan and evidence are, and whether you add a readiness review or need a POA&M close-out review. Compare the readiness review, assessment and close-out review fees separately, along with travel and expenses.
Related RFP templates
Download Template