Information Security Policy Template for IT (Free, Word)
A free, editable information security policy for small and mid-sized organizations, with data classification, access and password rules, AI tool use and…
Word · FreeDownload Template →
A free CMMC compliance checklist for defense contractors: every Level 1 and Level 2 requirement, with status, evidence, owner and POA&M fields, and an SPRS score that updates as you go.
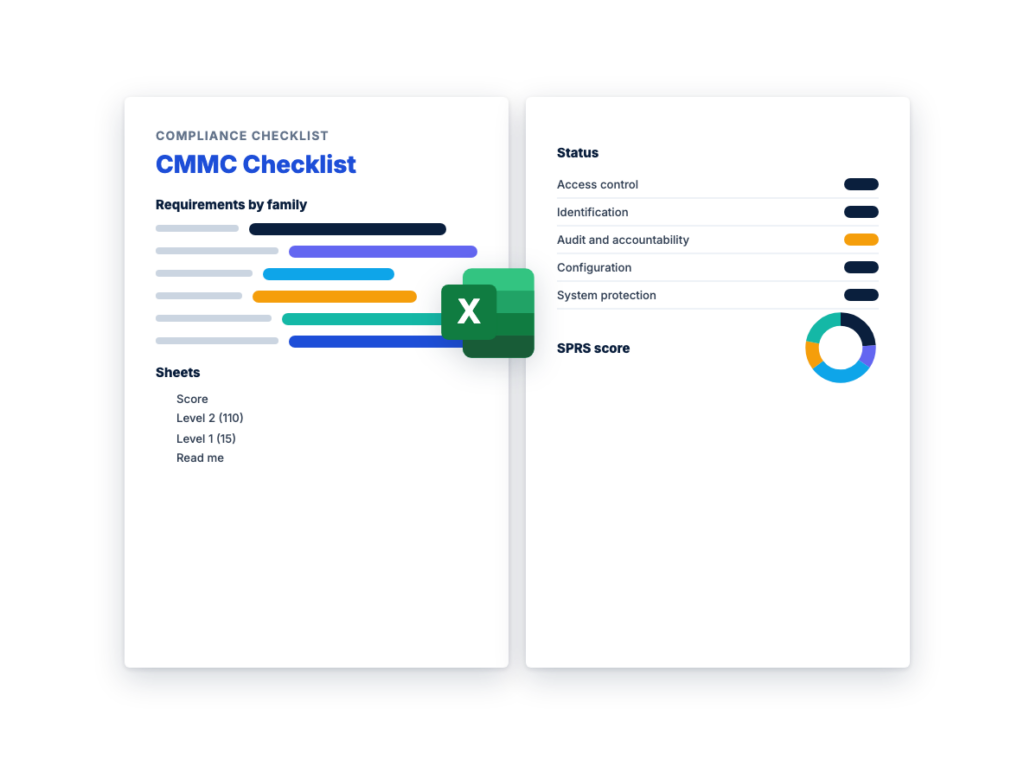
See an example before you download. The Excel file has every sheet listed below, ready to fill in, with instructions on its Read me sheet.
The sections in the document, in order.
This free CMMC compliance checklist puts every CMMC Level 1 and Level 2 requirement in one Excel workbook. Level 1 is the 15 basic safeguarding requirements in FAR 52.204-21, which match 17 NIST requirements. Level 2 is all 110 security requirements in NIST SP 800-171 Rev. 2, quoted word for word. For each requirement you record a status, the evidence, an owner and, where the rules allow one, a POA&M entry, and the SPRS score is calculated as you go.
The point values come from the CMMC scoring methodology in 32 CFR 170.24: 5, 3 or 1 points off a maximum of 110 for each requirement not met. They're the same values the DoD's NIST SP 800-171 assessment methodology uses for SPRS scores under DFARS 252.204-7019 and 252.204-7020. The checklist is for contractors and subcontractors that handle Federal Contract Information (FCI) or Controlled Unclassified Information (CUI), including IT and security firms that find DoD work on RFPhub's list of open federal IT and cybersecurity RFPs.
The checklist helps you prepare, but it isn't an assessment. Only an authorized assessor's result, or your own self-assessment and affirmation where the rule allows one, counts toward a CMMC status, and the score that counts is the one entered in SPRS.
Use the score calculator on this page, or download the Excel checklist for evidence, owners and POA&M dates.
Mark each NIST SP 800-171 requirement as Met, Not met or Not applicable, and the SPRS score updates as you go. Your marks stay in this browser only; nothing is sent anywhere. For evidence, owners and POA&M dates, use the Excel checklist.
Point values from 32 CFR 170.24; POA&M rules from 32 CFR 170.21. This calculator helps you prepare. It isn't an assessment: only your self-assessment and affirmation in SPRS, or an authorized assessor's result, counts.
Start with the level your solicitation or contract names. The Level 1 checklist and the Level 2 checklist are separate sheets. If you handle CUI, use the Level 2 sheet: it already includes the Level 1 requirements.
The SPRS score sums up how much of NIST SP 800-171 you’ve implemented, weighted by how much each requirement matters. The same 110-point scale is used for the DoD’s NIST SP 800-171 assessments under DFARS 252.204-7019 and 252.204-7020 and for CMMC Level 2 under 32 CFR 170.24. It works like this:
CMMC has three levels. This checklist covers Level 1 and Level 2. Level 3 adds selected requirements from NIST SP 800-172, is assessed by the government, and isn’t covered here.
Status as of November 2026: Phase 1 of the rollout began on November 10, 2025, when the DFARS CMMC rule took effect. Phase 2 would have added third-party (C3PAO) certification as a condition of award from November 10, 2026, but the Department of War suspended it on July 13, 2026, and the DoD CIO’s CMMC page says the program is paused in Phase 1. During the suspension, solicitations may only require Level 1 (Self) or Level 2 (Self), and DFARS 252.204-7012 still applies. Check that page before you rely on any date.
How the two levels compare:
You start at 110, one point for each NIST SP 800-171 requirement, and subtract 5, 3 or 1 points for each requirement not met, depending on its value in the DoD scoring methodology. Multifactor authentication and FIPS-validated encryption cost 3 points instead of 5 if they’re partly in place. The score can go as low as -203, and without a system security plan there’s no score at all.
Yes, when the solicitation requires Level 2 (Self): you assess all 110 requirements, enter the score in SPRS and affirm it, with a new assessment every three years and an affirmation every year. The rule also lets DoD require a third-party C3PAO assessment for Level 2 instead. Since July 13, 2026, with Phase 2 suspended, DoD solicitations may only require Level 1 (Self) or Level 2 (Self), so check the current status before you plan around a date.
A plan of action and milestones (POA&M) lists the requirements you haven’t met yet, with the fix, the owner and the dates. At Level 2 it lets you reach a conditional status if you score at least 88 of 110 and only 1-point requirements are open, plus 3.13.11 when encryption is used but isn’t FIPS-validated, and none of six named requirements is on it. You must close it out within 180 days or the conditional status expires, and Level 1 doesn’t allow POA&Ms at all.
Level 1 protects Federal Contract Information with the 15 basic safeguarding requirements in FAR 52.204-21: limiting system access, controlling external connections and public posting, identifying and authenticating users, sanitizing media, physical access controls, boundary protection, separating public systems, fixing flaws and protecting against malicious code. They match 17 NIST SP 800-171 requirements. You self-assess every year, every requirement must be met, and POA&Ms aren’t allowed.
Every year for Level 1 and every three years for Level 2 (Self), with the results entered in SPRS. A senior company official also affirms compliance in SPRS after each assessment and every year, and a Level 2 status lapses if the annual affirmation isn’t made. Update the checklist whenever your systems change, so the next assessment starts from an accurate picture.
A free, editable information security policy for small and mid-sized organizations, with data classification, access and password rules, AI tool use and…
A free, vendor-neutral business continuity plan template in Word, with a BIA worksheet, process priorities, continuity strategies, crisis management, communications and an…
A free, vendor-neutral incident response plan template in Word, with roles, a severity matrix, out-of-band contacts, containment approvals, playbooks, evidence and notification…
Please provide your feedback below.
"*" indicates required fields