C3PAO Assessment RFQ Template (Free): CMMC Level 2
A free C3PAO RFQ for a CMMC Level 2 certification assessment: paste-ready requirements for scope, team, independence and pricing, provider questions and…
Word · FreeDownload Template →
Paste-ready vCISO requirements (scope, named lead, deliverables, independence, handover and pricing), questions that separate providers, and a weighted scoring rubric.
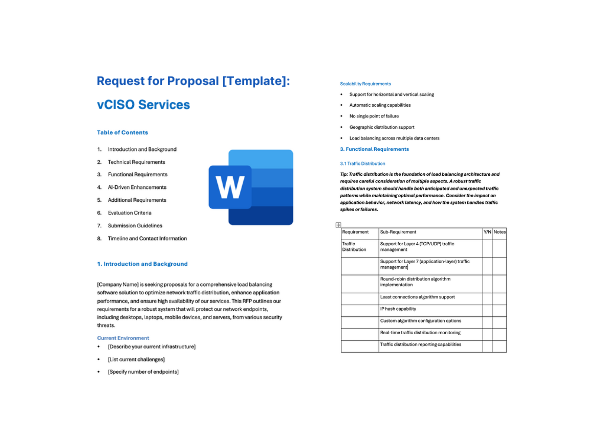
See the structure before you download. The Word file has every section listed below, ready to fill in.
The sections in the document, in order.
Use this vCISO RFP template when you're hiring a virtual or fractional CISO: a named, part-time security leader who owns your security program, leads your compliance work and reports on cyber risk to your leadership and board.
You're buying one person's judgment and time, so the template puts the named lead, the first-phase plan and independence from product sales at the center.
It's written for the executive sponsor, IT lead and procurement team running the selection, and it covers when to issue an RFI first, the requirements to send, the questions that separate providers, and how to score the answers.
Download the editable Microsoft Word version below. Every requirement, provider question and scoring weight on this page is in the document, ready to tailor and send.
Choosing a vCISO is a hiring decision as much as a purchase: the person you pick will sit with your leadership, see your weaknesses and speak for your security program to customers, auditors and the board. The example schedule in this template runs about nine weeks from kickoff to a signed engagement; allow less for a fixed-scope assessment, and more if your board must approve the engagement.
Each line is written to paste straight into your RFP. Must-have means a provider that cannot meet it is out; Nice-to-have earns extra points. Change the priorities to fit your situation, and delete what doesn't apply.
| ID | Requirement | Priority |
|---|---|---|
| S1 | Leadership of our security program as our CISO for the contract term: setting priorities, owning the security policies and roadmap, and making or recommending decisions within the authority we define. State which decisions the vCISO would expect to make and which they would put to our executives. | Must-have |
| S2 | An initial assessment of our security program against a framework we agree, such as NIST CSF [if applicable], covering governance, people, processes and technology, based on interviews with our leadership, IT staff and providers and a review of our current tools, configurations and documents. | Must-have |
| S3 | A risk assessment and a risk register that records each risk with a rating, an owner, a treatment decision (reduce, accept, transfer or avoid) and a target date, kept current for the whole engagement and reviewed with our leadership on a schedule we agree. | Must-have |
| S4 | A security roadmap ranked by risk reduction, with a budget estimate for each item covering internal effort, tools and outside services, aligned with our budget cycle and updated when priorities change. | Must-have |
| S5 | Writing or updating our security policies and standards (for example information security, acceptable use, access control, data classification and handling, incident response, vendor risk, and backup and recovery), mapped to the frameworks in scope, with a scheduled review and approval cycle. | Must-have |
| S6 | Leadership of our compliance program for the frameworks that apply to us: SOC 2 [if applicable], ISO/IEC 27001 [if applicable], HIPAA [if applicable], PCI DSS [if applicable], CMMC [if applicable] and NIST CSF [if applicable]. This covers gap assessment, a remediation plan, assigning control owners, evidence collection and coordination with our auditor or assessor. | Must-have |
| S7 | Answering, or reviewing our answers to, security questionnaires and audits from customers, prospects and our cyber insurer; building and maintaining a library of approved answers and supporting documents; and joining customer security review calls when we ask. State the turnaround you commit to. | Must-have |
| S8 | Oversight of our MSP, MSSP or MDR provider and other security vendors: reviewing their scope, contracts and service-level reports, holding them to their commitments, and running security reviews of new vendors before we sign with them. | Must-have |
| S9 | Writing or updating our incident response plan and playbooks, covering roles, decision authority, escalation, contacts for our legal counsel, cyber insurer and outside incident response firm, and our notification duties to regulators, customers and others. | Must-have |
| S10 | Tabletop exercises for our executives and for our technical teams, run on a schedule we agree, each followed by a written after-action report with assigned follow-up items. | Must-have |
| S11 | A defined role for the vCISO during a security incident, such as coordinating the response, advising executives on decisions, and working with our counsel, insurer and incident response firm. State what the vCISO does not do (for example hands-on forensics) and who does it. | Must-have |
| S12 | Oversight of our security awareness program: setting the training plan and phishing simulations, tracking completion and results, and reporting them to leadership. State whether you run the program or oversee whoever does. | Must-have |
| ID | Requirement | Priority |
|---|---|---|
| L1 | The name of the person who will act as our vCISO, with a CV showing the security leadership roles they have held, the industries and company sizes they have served, and the frameworks they have led programs against. | Must-have |
| L2 | The named lead is the person we interview and the person who leads the engagement. The provider will not substitute them without our written approval, and if they leave the firm, it will propose a replacement with comparable experience for us to interview. | Must-have |
| L3 | Experience leading security programs for organizations in our industry and of our size, with the frameworks in scope, and in presenting to boards or audit committees, supported by references from clients the named lead served directly. | Must-have |
| L4 | A list of everyone else who would work on our account (for example analysts, compliance specialists or policy writers), their roles and experience, and a clear split of which tasks the named lead does personally and which others do. | Must-have |
| L5 | A named backup who knows our program and covers the named lead's absences, holidays and conflicting commitments, with handovers between them at no extra charge. | Must-have |
| L6 | A statement of how many other clients the named lead serves at the same time, and how our time and response commitments are protected when another client has an incident. | Must-have |
| ID | Requirement | Priority |
|---|---|---|
| D1 | A first-phase plan listing each deliverable, its format and its due date, and the date the first phase ends, agreed in the statement of work. | Must-have |
| D2 | An assessment report with a short executive summary written for non-technical leaders, and a detailed findings list giving the severity, the evidence and the recommended fix for each finding. | Must-have |
| D3 | Written status reports to our executive sponsor on a schedule we agree, covering roadmap progress, changes to the risk register, decisions needed, issues with providers, and time used against the retainer. | Must-have |
| D4 | Briefings for our board or its audit or risk committee, prepared and presented by the named lead, covering cyber risk, program progress, incidents and the decisions the board is asked to make, in plain language. | Must-have |
| D5 | A set of security measures agreed in the first phase (for example MFA coverage, patching timeliness, open high-rated risks and training completion), tracked over time and tied to the roadmap. | Must-have |
| D6 | All deliverables in editable formats, stored in our own document systems, so we keep them whether or not the engagement continues. | Must-have |
| D7 | A customer-facing security overview and a standard document pack that our sales team can share with prospects, kept current as the program changes. | Nice-to-have |
| ID | Requirement | Priority |
|---|---|---|
| N1 | Confidentiality terms covering everything the provider learns about our security weaknesses, systems and customers, with our data held only on systems we approve and returned or destroyed at the end of the engagement. | Must-have |
| N2 | Access to our systems only through accounts we issue to named individuals who have passed background checks in line with our hiring standards, with MFA and the least privilege needed, no shared accounts, and all access removed when the engagement ends or a person leaves the account. | Must-have |
| N3 | A description of the provider's own security program, including how it protects client data, keeps each client's information separate and secures staff devices, plus any independent attestation or certification it holds, such as a SOC 2 report or ISO/IEC 27001 certification [if applicable]. | Must-have |
| N4 | Disclosure of every security product, service or firm from which the provider or the named lead earns resale margin, referral fees, commissions or partner incentives, and a commitment to disclose any such interest in writing before recommending it to us. | Must-have |
| N5 | Disclosure of any ownership, partnership or commercial relationship with our current MSP, MSSP, auditor or other security providers [list them], since the vCISO will oversee their work. | Must-have |
| N6 | Product-neutral recommendations: where we need a product or service, the vCISO presents options from different suppliers where they exist, with the reasons for the recommendation and its full cost. | Must-have |
| N7 | A statement of whether the provider or an affiliate offers audit, assessment or certification services. The provider will not audit, assess or certify controls it designed or operates for us. | Must-have |
| N8 | Professional liability (errors and omissions) and cyber liability insurance with the coverage limits stated, and a commitment to notify us of any security incident at the provider that affects our data within a defined time. State the time. | Must-have |
| ID | Requirement | Priority |
|---|---|---|
| E1 | The engagement model proposed (ongoing retainer, fixed project, interim CISO, or a fixed first phase followed by a retainer), the initial term, renewal terms, and the notice period for either side to end the engagement. | Must-have |
| E2 | An onboarding plan covering kickoff, stakeholder interviews, access requests, document collection and introductions to our MSP, MSSP, auditor and other key providers. | Must-have |
| E3 | A working rhythm with regular meetings with our executive sponsor and IT lead, a single channel for requests, and committed response times for routine requests and urgent issues. State the response times. | Must-have |
| E4 | A way to reach the named lead or backup outside business hours during a security incident, with a committed response time and a clear statement of how incident time is charged. | Must-have |
| E5 | On-site attendance when we need it, such as board meetings, tabletop exercises and audits at [locations], with travel agreed in advance. | Nice-to-have |
| E6 | Ownership by us of all documents, policies, registers, reports and other work produced for us, with a lasting license for our internal use of any provider templates they are built on. Any compliance tool or document workspace used for our program is licensed in our name, or our data in it can be exported in full in a standard format at any time. | Must-have |
| E7 | A handover at the end of the engagement to our new CISO or another provider: an index of documents, open risks and actions, projects in progress, provider contacts, and a list of the access the provider held, with a handover period. State its length and cost. | Must-have |
| E8 | Help hiring a full-time CISO or security staff when we're ready: drafting the role, joining interviews and planning the handover to the new hire. | Nice-to-have |
| ID | Requirement | Priority |
|---|---|---|
| C1 | A fixed fee for the initial assessment, risk register and roadmap, stating what's included and what would change the fee. | Must-have |
| C2 | A monthly retainer that states how much of the named lead's time is included, and how that time is measured and reported to us. | Must-have |
| C3 | Hourly or daily rates for the named lead and each other role for work beyond the retainer, with no extra time billed unless we approve it in writing first. | Must-have |
| C4 | Rules for unused retainer time (whether it carries over, and for how long), for time above the retainer during busy periods such as an audit or an incident, and for changing the retainer level with notice. | Must-have |
| C5 | Separate prices for optional services, such as on-call incident availability, audit preparation, tabletop exercises, policy development and running the awareness program. | Must-have |
| C6 | A cap on rate increases at renewal. State the cap. | Must-have |
| C7 | Termination for convenience by either side with written notice, with fees limited to work done and the agreed handover period, and no termination penalty. | Must-have |
These questions are designed to separate providers, not to collect brochure answers. Ask for evidence: a sample deliverable, an interview with the named lead or a reference.
Score each criterion from 1 to 5, multiply by its weight, and add the results. The weights below are a starting point; agree on your own before any proposals arrive so the scoring can't be bent around a favorite.
| Criterion | Weight | What a strong response shows |
|---|---|---|
| Named lead's fit and experience | 25% | Security leadership experience in your industry, at your size and with your frameworks, a strong interview without the sales team, and references from clients the named lead served directly. |
| Quality of the first-phase plan | 20% | Specific, dated deliverables, a sensible choice of framework, a clear list of what's needed from your team, and sample deliverables that show what you'll receive. |
| Judgment in the scenarios | 15% | Practical, honest answers to the questionnaire, board, incident and MSSP scenarios, with clear priorities and a realistic view of the vCISO's role. |
| Reporting and communication | 10% | Status reports and board briefings in plain language that you would be comfortable putting in front of your board, with measures tied to the roadmap. |
| Independence and conflicts | 10% | Full written disclosure of resale, referral and partner fees and of relationships with your providers, product-neutral recommendations, and separation from audit work. |
| Engagement terms and handover | 10% | A named backup, clear response times, your ownership of documents and accounts, a reasonable notice period and a credible handover plan. |
| Commercials and value | 10% | Clear pricing for the first phase and the retainer, a defined amount of the named lead's time, fair rules for extra and unused time, and a transparent rate card. |
| Total | 100% |
Scoring scale
Your background and what's driving the need; the scope of services, from risk assessment and roadmap to compliance, provider oversight, customer questionnaires, incident response planning and board reporting; requirements for the named lead and team, deliverables, confidentiality and independence, each marked Must-have or Nice-to-have; questions and scenarios that show how each provider works; engagement, handover and pricing terms; and the rubric you'll score with. This template includes all of them.
Price depends on scope, so the only useful comparison is between proposals priced against the same scope. The main cost drivers are how much of the named lead's time you need each month, how many frameworks and audits are in scope and how soon they fall due, how regulated your industry is, the size and complexity of your environment, whether the vCISO must be on call for incidents, and whether any work must happen on site. Compare the fixed first-phase fee, the retainer and the rates for extra time separately in the pricing table.
An MSSP (managed security service provider) runs security operations for you, such as monitoring alerts and managing security tools, under a service contract. A vCISO is a security leader who sets priorities, owns the security program and its policies, reports to your leadership, and decides what you need from providers such as an MSSP. The roles complement each other: a vCISO can oversee an MSSP's work and hold it to its service levels. If a firm offers both, ask how its vCISO stays independent when reviewing a colleague's service.
Not by title: SOC 2 doesn't require a CISO or a vCISO. It does expect clear responsibility for security, and controls that are designed, operating and backed by evidence the auditor can test, which is hard to achieve without someone who owns the program. A vCISO can lead the readiness work: scoping the report, writing policies, assigning control owners, collecting evidence and working with the auditor. Keep the roles separate, because the CPA firm that examines your controls must be independent of them and shouldn't be the firm that designed them.
 BARR Advisory
 BD Emerson
 BPM
 CBIZ Pivot Point Security
 CBTS
 Centric Consulting
 CISO Global
 Coalfire
 DAG Tech
 eSentire
 Fortium Partners
 Fractional CISOFFRSecure
 GuidePoint Security
 Hartman Executive Advisors
 Kroll
 Kudelski Security
 LRQA
 Netrix Global
 Network Right
 Optiv
 Palo Alto Networks
 Performance Improvement Partners
 Petronella Technology Group
 PKF O'Connor Davies
 RSM US
 SideChannel
 TechCXOTThrive
Listed A to Z from vendors' own descriptions. Listings are free, unranked and not an endorsement. See all vCISO providers →
A free C3PAO RFQ for a CMMC Level 2 certification assessment: paste-ready requirements for scope, team, independence and pricing, provider questions and…
Paste-ready requirements for finding and securing service accounts, API keys, tokens, workload identities and AI agents, with vendor questions, a scoring rubric…
Paste-ready requirements for immutable backup storage and cyber recovery vaults (object lock, isolation, multi-person approval, clean-room recovery), vendor questions and a weighted…
Please provide your feedback below.
"*" indicates required fields